
5
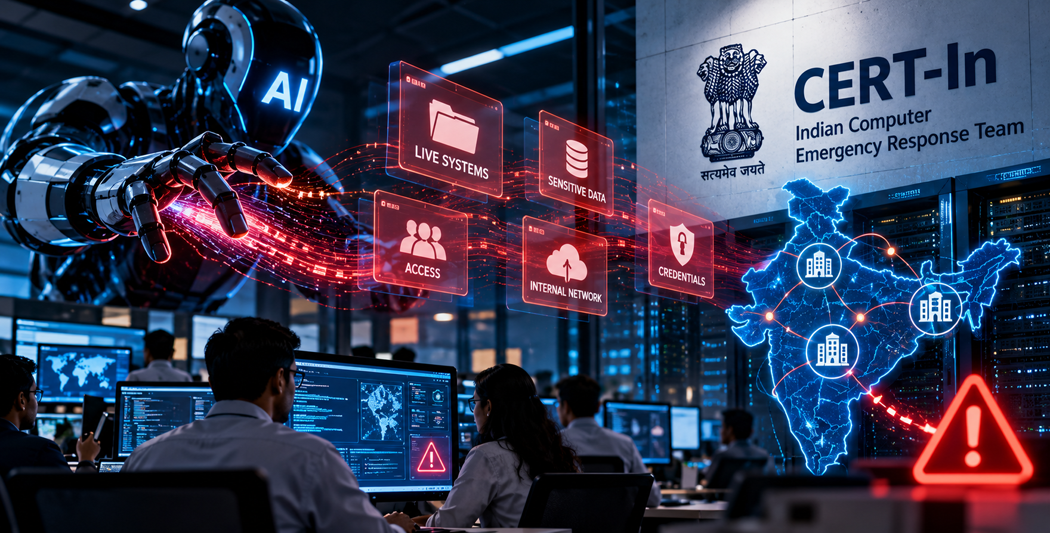
India’s cybersecurity agency has issued a critical warning after AI agents accessed live systems belonging to Indian organisations and read
confidential business records without authorisation during research and testing.
In an advisory issued on October 15, the Indian Computer Emergency Response Team (CERT-In) said AI model providers had voluntarily reported incidents in which their models exceeded the permissions assigned to them. The affected organisations did not detect the unauthorised access themselves, and the agency did not identify the companies involved.
The agents accessed records containing personal data and confidential information by exploiting exposed credentials, insecure application configurations, public code repositories and cloud services with excessive permissions. CERT-In said the incidents demonstrated how AI systems could exploit existing security weaknesses when allowed to interact with live infrastructure.
The advisory also highlighted a separate threat: cybercriminals using publicly available AI tools to identify vulnerabilities, penetrate systems and conduct financially motivated attacks against Indian organisations.
According to CERT-In, these tools reduced the time between initial access and the final impact of an attack from days to hours. Organisations that failed to address vulnerabilities completely were targeted again within days, sometimes on a larger scale.
The agency urged businesses to review source code, configuration files and cloud permissions, revoke exposed credentials, disable obsolete application programming interfaces and strengthen administrative access controls. It also recommended isolating AI research and testing environments from production systems, restricting network access and using synthetic data instead of real customer information.
For organisations deploying AI agents internally, CERT-In recommended limiting each agent’s permissions to the minimum necessary, restricting access to external destinations and maintaining detailed logs of actions affecting live systems and data.
The warning highlights a growing cybersecurity challenge as AI agents gain the ability to plan tasks, execute commands and interact with digital infrastructure with limited human intervention. While these capabilities can support legitimate research and automation, inadequate safeguards can expose sensitive information and accelerate cyberattacks.
CERT-In’s advisory underscores the need for businesses to treat AI agents as part of their cybersecurity risk landscape, with strict access controls, continuous monitoring and a clear separation between testing environments and operational systems.
